Showing posts with label Hackers. Show all posts

Thursday, 19 December 2013

Nowadays it’s easy to hack a website in just four steps

Hackers (extremexploit.com)

Till yesteryears it required Tech Geeks to have an above average knowledge to hack a website but these days it has become a child’s play. Like conventional searches, you can Google out the tools required to plan a Hack-Attack on a website and with a little effort you can execute the same with ease. Here it is, in 4 easy steps, how hackers execute it.

Step 1: Identifying

The Hacktivists first identify their target website which they want to attack upon. They first qualify the website, according to the vulnerability level, they wish to attack. Checking the vulnerability of the website allows the hacker to prepare tools and techniques required to bring down the website.

Hackers generally use Google Dork, or Google Hacking, to execute a vulnerability check against these easy-to-hack websites. It was very recent that a hacker posted a list of 5,000 such websites which were really easy to be attacked. If they don’t wish to Google it out, they can Bing it. This tool is heaven for hackers as it helps in qualifying such websites.

Hackers have a ready-to-refer index of Dorks which points out the websites having a particular vulnerability. Right from passwords to Login credentials, there is Dork available for everything. They would Google “intitle:”Index of” master.passwd” which will return them a file containing the passwords and then they have the list of potential victims ready with them to execute the hack.

Step 2: Spotting the vulnerabilities

Acunetix – a Windows based application to test the website – developed by a UK based company, was designed and is still in prominent use by developers to test the vulnerabilities in the website, but the technical expertise of hackers to this tool allows them access to point out the weakness levels of the website. Once the site is identified for attack, this tool is used by hackers to check the vulnerability of the website, as all websites qualified in level 1 may not be susceptible to attack.

Since the hackers have in-depth knowledge of the above mentioned software, they can not only crack the version from a trial one, but the cracked version is also available freely amongst the hacker community. Once they enter the URL or website address in this software they are able to point out the loopholes in the website and all they do is, move to step 3.

Step 3: The Attack on the website – SQL Injection

The SQL injection is the easiest and the most used way by hackers to hack into a website. It is used by hackers to hack into user accounts and steal information stored into its databases. This attack aims at information stealing using some lines of code of SQL (Structured Query List) which is a database programming language. The hacker’s don’t even have to learn the language for this attack, as there is an available software called “Havij” in the hacker forums where it is available free of cost. It comes as an easily useable application. Havij is originally a development from Iran. The word itself means carrot, a bad-slang for the word penis, ultimately meaning that the hack-ware helps penetrating a website.

Havij has 2 versions – paid and unpaid, both of them differential in powers of penetrating, although the paid version can be cracked and downloaded from other hacker forums. The interface of this software completely simple like any other windows application, which does its work when a newbie hacker just copies the link of the website needed to hack and pastes it into the application.

The tasks Havij can perform are very surprising. The best one for them and worst for the users of the website is called “Get”. It fetches all the data stored in the target website’s databases which range from usernames, passwords to phone numbers and bank details.

It is so easy for hackers that within a couple of minutes of their time, in which they can search, download, and use one or two automated hack-wares that allows them to access websites which are vulnerable to such attacks. Very much assured, that the websites of high profile companies like Google, Microsoft and Facebook are completely safe from such tools. As mentioned before, the vulnerability of the web is displayed by the attack made on Sony’s PlayStation Network which led to the leaking of their customers’ personal information in a very similar way.

Step 4: The DDoS – The A Game

SQL Injection has been used by the infamous hacktivist community – Anonymous for over a year now, but they tend to go forth with the DDoS when simple tools like the Havij don’t work. Again like the SQL (pronounced Sequel) Injection attack there are freely available tools for the DDoS as well.

As it appears, the DDoS is also as simple as the SQL Injection attack. The program used here is called the Low Orbit Ion Cannon (LOIC), which was brought to life by web developers for stress testing their own websites, but was later hijacked by hackers to attack the websites for non-social use.

The LOIC is available to the hackers freely on the website Source Forge. Again as simple as the Havij, the hackers just have to type in the link of the website they want to DDoS and the application does the rest. LOIC overloads the server of the target website with upto 200 requests per second.

Now again, the bigger websites can easily cope up with this type of an attack without crashing, most of the other websites cannot. Surely if a group of hackers, although newborn, dedicates itself to the job, it is very easy for them to complete it.

This type of technology horrifies the readers, but it is very simple to use by the hackers that they can even control it from their phones, meaning that they could well be watching a movie with their buddies in the cinema while attacking the website they want to bring down.

This is not an exhaustive list and processes how the hackers execute the act but there are many a tutorials on various hacking forums that teach how to perform the attack. There is no end to this notoriousness, in many cases a heinous crime, which has caused a loss of millions and millions of dollars to the world. So are you going to get your website checked through your developer today? May be today would be a real good day to get it done.

Friday, 8 November 2013

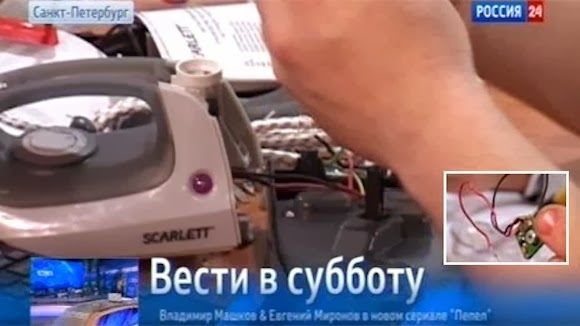
Russia: Chinese planting hidden chips in Irons & electric kettles which serve malware in systems

Chinese hidden chip in iron


How will you react when you will came to know—your Chinese Iron has inbuilt chip which is being used to server malware on to your systems, well if you talk mine then i will throw that outside and will call that “The NSA Aunty.”

A Russian TV Rossiya 24 reported about this Malware machine even they showed footage of technician while opening the Iron included in a batch of Chinese imports to find a “spy chip” with what he called “a little microphone”.

These types of hidden chips are being used to spread viruses through connecting to any computer with in a 200m (656ft) radius which were using unprotected Wi-Fi networks. Other components like mobile phones and car dashboard cameras are also affected with this hidden chip, the Russian TV reported.

One thing also reported by the channel that these hidden chips look small, but had been attacked company networks, sending out spam without administrators’ knowledge.

According to a news agency the latest order of these irons have been cancelled but more than 30 devices had already been sent to retailers in St. Petersburg.

From now, would you like to bring that NSA aunty to your home, tell us in comments, we like to hear from you.

Wednesday, 30 October 2013

iOS apps vulnerable to HTTP Request Hijacking attacks over WiFi

iOS apps vulnerable to HTTP Request Hijacking
Security researchers Adi Sharabani and Yair Amit have disclosed details about a widespread vulnerability in iOS apps, that could allow hackers to force the apps to send and receive data from the hackers' own servers rather than the legitimate ones they were coded to connect to.
Speaking about the issue at RSA Conference Europe 2013 in Amsterdam, researchers have provided details on this vulnerability, which stems from a commonly used approach to URL caching.

Demonstration shows that insecure public networks can also provide stealth access to our iOS apps to potential attackers using HTTP request hijacking methods.
The researchers put together a short video demonstrating, in which they use what is called a 301 directive to redirect the traffic flow from an app to an app maker’s server to the attacker’s server.

There are two limitations also, that the attacker needs to be physically near the victim for the initial poisoning to perform this attack and the flaw works only against HTTP traffic.

“A victim walks into Starbucks, connects to the Wi-Fi and uses her favorite apps,” explains an example. “Everything looks and behaves as normal, however an attacker is sitting at a nearby table and performs a silent HRH attack on her apps. The next day, she wakes up at home and logs in to read the news, but she’s now reading the attacker’s news!”

They estimate that at least 10,000 iOS apps in the Apple App Store are vulnerable to the hack. As a result, apps that display news, stock quotes, social media content, or even some online banking details can be manipulated to display fraudulent information and intercept data sent by the end user.
Victims can uninstall apps to scrub their devices clean, and Skycure has released app code that prevents the web caching from taking place. It may be a while until developers can get this fix implemented, so connect to those public networks with extreme caution.

Tuesday, 15 October 2013

Antivirus firm ESET and BitDefender website defaced by Pro-Palestinian Hackers

A pro-Palestinian hacktivist group 'KDMS Team', who recently managed to briefly hijack the Metasploit website of security firm Rapid7 and become popular after Hacking World's largest Web Hosting Network Leaseweb website and antivirus vendors AVG, Avira as well as mobile messaging service WhatsApp's websites.

Now even I have to say that - Security is just an Illusion, because just now the group aligned with Anonymous has successfully hijacked another two Antivirus firm website - ESET and Bitdefender.
The KDMS Team successfully changed the DNS records of both sites to redirect people to a website playing the Palestinian national anthem and displaying a political message under the title "You Got Pwned".
Message posted on Bitdefender and Eset website says:
Hello bitdefender
Touched By KDMS team
We was thinking about quitting hacking and disappear again ..!
But we said : there is some sites must be hacked
You are one of our targets Therefore we are here ..
And there is another thing .. do you know Palestine ?
There is a land called Palestine on the earth This land has been stolen by Zionist Do you know it ?
Palestinian people has the right to live in peace Deserve to liberate their land and release all prisoners from israeli jails We want peace Long Live Palestine
Both affected domains are registered from REGISTER.COM, INC. by companies, which is also a domain registrar for Metasploit website -- was hijacked yesterday via a spoofed change request faxed to Register.com. But the technical details on how hackers managed to hijack the ESET and Bitdefender website is not yet available, we are in contact with hackers.. Will update the article in a few hours. Stay Tuned !
Defacement of Security companies is really embarrassing and hacker's tactics allowed them to get their political message to millions of users. One of their team members tweeted, "When it's a matter of resistance no one will blame you. . Free Palestine .. Fight for Palestine"

Scammers once again take Advantage of Deepavali Festival

Deepavali
CyberCriminals always try to take advantage of festivals.  As expected, cyber criminals have started to sending Diwali themed scam emails.  Diwali/Deepavali is a Hindu festival which is being celebrated in Nov 2,this year.

One of the scam email spotted by Symantec experts which is purportedly from Reserve Bank of India(RBI) informs the users that they have been awarded a prize of 4 crore and 70 Lac Indian rupees(US$763,609) as a Diwali celebration promotion.

"Dear Lucky Winner, The Reserve Bank of India(RBI) Governor, Secretary-General of the United Nations met with the Senate Tax committee on Finance RBI Mumbai/Delhi branch. You have been awarded the total sum of 4 Crore, 70 Lac Indian Ruppes in the up-coming diwali celebration promotion " The scam email reads.

The recipients are asked to contact the RBI Regional director by sending email to a given email address to claim their winnings. Keep in mind, there is no such kind of promotion.

Those who contact the scammers either will be asked to pay certain fees to get the prize money or will be asked to give certain personal/financial information.

Tuesday, 8 October 2013

WhatsApp Website defaced by KDMS team

WhatsApp Defaced Page
WhatsApp Defaced Page          
The Web site of WhatsApp, a widely used messaging app, appeared to have been defaced Tuesday.
The site showed a pro-Palestinian message at 2:40 a.m. PT Tuesday and was given the title "You Got Pwned." A group called KDMS Team claimed credit for the attack.

According to the Whois database, which can be used to see what numeric Internet Protocol (IP) address is assigned to a given Internet domain, the whatsapp IP address record was changed on Tuesday. Such a change, made through the Internet's Domain Name Service (DNS) system, is one way that users who typed in the whatsapp.com name would be redirected to a different Web site.
It wasn't immediately clear if there were any problems with WhatsApp's customer data or services. CNET contacted the company for comment and will update this story with its reply.
WhatsApp is used to send billions of messages a day using mobile apps.

AVG Antivirus and Avira Websites defaced by Palestinian Hackers

AVG Antivirus Hack Screenshot

The Website of Word's most popular Antivirus Firm - AVG were hacked this morning and defaced by a new Palestinian Hacker group - KDMS Team, affiliated with Anonymous Group.
The Defacement page titled 'You got Pwned', with Anonymous Logo and playing Palestinian national anthem in the page background, says: 

we want to tell you that there is a land called Palestine on the earth
this land has been stolen by Zionist
do you know it ?
Palestinian people has the right to live in peace
Deserve to liberate their land and release all prisoners from israeli jails
we want peace
and "There Is No Full Security We Can Catch You !"
Avira Website Defaced Page

Wednesday, 2 October 2013

16-Year School boy arrested for World's biggest cyber attack ever

16-Year School boy arrested for World's biggest cyber attack ever

16-Year-Old Teenager has been arrested over his alleged involvement in the World's biggest DDoS attacks against the Dutch anti-spam group Spamhaus.
 
The 16-year-old was detained by detectives at his home in south-west London after “significant sums of money” were found to be “flowing through his bank account”. He was also logged on to what officials say were “various virtual systems and forums” & had his computers and mobiles seized as officers worked through the night to secure potential evidence.

A DDoS attack takes place when hackers use an army of infected computers to send traffic to a server, causing a shutdown in the process.

It's unclear what role the teenager played in the massive distributed denial of service (DDoS) attack. The boy has been released on bail until later this year. A 35-year-old Dutchman was detained and his computers, data carriers and mobile phones were seized, local media speculates that the person is none other than CyberBunker spokesman Sven Olaf Kamphuis.

Saturday, 7 September 2013

FBI Cyber Division put 'Syrian Electronic Army' Hackers in wanted list


FBI Cyber Division put Syrian Electronic Army Hackers in wanted list

 
The Syrian Electronic Army (SEA), a pro-regime hacker group that emerged during Syrian anti-government protests in 2011, and involved in cyber attacks against western media organizations are now in the FBI's wanted list.

The Federal Bureau of Investigation has issued an alert warning of cyber attacks by the Syrian Electronic Army and finally put them on its radar. "The SEA'S primary capabilities include spear-phishing, web defacements, and hijacking social media accounts to spread propaganda." they said. The FBI also has increased its surveillance of Syrians living in the US.
According to some anti-Assad activists, the group was founded by former intelligence agents and hardcore Assad supporters. SEA had compromised social media profiles for Western news organizations by sending fake email messages to news staff in an attempt to gain access to login credentials.
 
FBI Cyber Division put Syrian Electronic Army Hackers in wanted list

Most recently, the group grabbed international attention after commandeering the websites of the New York Times, Washington Post and this week the recruitment website for the US Marine Corps.

The group's was able to compromise the multiple Associated Press (AP) Twitter feeds, then using them to issue bogus messages, including the following alert on April 23 i.e. "Breaking: Two Explosions in the White House and Barack Obama is injured." In the wake of that tweet, the White House confirmed that the president was unharmed, that there had been no explosions and that the FBI was investigating the hoax tweets.

So how did the SEA get better in only a few months? ''I don't think it would be unreasonable to suspect someone more skilled is helping them out,'' says Adam Myers, vice president of intelligence for security firm CrowdStrike.

Is the Syrian Electronic Army based in Syria? After Syria reestablished its Internet connection last week, following a blackout that lasted approximately 24 hours. Security Experts noticed that Syrian Electronic Army Hackers were online on twitter. These kinds of cuts do not affect the terrorists operating in Syria as they have their own US-supplied communication equipment.

The Syrian Electronic Army has multiple domains seized by its domain registration firm. Interestingly, The Syrian Electronic Army's first domain name was registered by the Syrian Computer Society, hosted on the network of the Syrian government.

“Please maintain heightened awareness of your network traffic and take appropriate steps to maintain your network security,” the FBI memo said. FBI request anyone who suspects they're under attack to call its CyWatch division at 855-292-3937.

Researchers Discover 'Hesperbot' - A New and Potent Banking Trojan


Hesperbot   A New Banking Trojan that can create hidden VNC server on infected systems

 
Security firm ESET has discovered a new and effective banking trojan, targeting online banking users and designed to beat the mobile multi-factor authentication systems.
Hesperbot detected as Win32/Spy.Hesperbot is very identical to the infamous Zeus and SpyEye Banking Malwares and infects users in Turkey, the Czech Republic, Portugal, and the United Kingdom.
Trojan has functionalities such as keystroke logging, creation of screenshots and video capture, and setting up a remote proxy.

The attackers aim to obtain login credentials giving them access to the victim’s bank account and getting them to install a mobile component of the malware on their Symbian, Blackberry or Android phone.
Some other advanced tricks are also included in this banking Trojan, such as creating a hidden VNC server on the infected system and can do network traffic interception with HTML injection capabilities.
The trojan also harvests email addresses from the infected system and sends them to a remote server. It is possible that these collected addresses were also targeted by the malware-spreading campaigns.
 
So far, the Trojan hasn't spread too far. The campaign was first detected in the Czech Republic where the attackers had used phishing emails impersonating the country’s postal service. Armed with this information, the crooks can try to log into victims' online bank accounts to siphon off their cash.

As for the UK, a special variant of the malware has been created, but ESET said it could not provide any further detail on it.

Hacking Facebook to delete any account; Facebook again refuses to pay Bounty


Hacking Facebook to delete any account; Facebook again refuses to pay Bounty

In the past few days, Facebook refused to pay bounty to Khalil Shreateh, the security researcher who used the bug he discovered to post directly on Facebook CEO Mark Zuckerberg’s Timeline after Facebook Security rejected his attempts to report it.
Ehraz Ahmed, an independent Security Researcher claimed that he reported a critical vulnerability to the Facebook Security team, which allows the attacker to delete any account from Facebook.
But Facebook refuses to Pay Bug Bounty, because he tested flaw once on his friend's account, "I reported this bug to Facebook, I'm really not happy with them. After waiting for such a long time for their reply, they denied it saying that you used this bug only works for test accounts, where as I used it for removing real accounts and now the vulnerability is also fixed after their email." he said on his blog.
Vulnerable URL:
https://www.facebook.com/ajax/whitehat/delete_test_users.php? fb_dtsg=AQA1E-WE&selected_users[0]=[Victems Profile ID]&__user=[Attackers Profile ID]&__a=1
Where selected_users[0] and __user parameters are vulnerable to run exploit.
 

Secunia launches the next generation of Complete Patch Management: The Secunia CSI 7.0


Patch Management

Cybercrime costs organizations millions of dollars and to protect business from the consequences of security breaches, vulnerability intelligence and patch management are basic necessities in the toolbox of any IT team, as emphasized by organizations like the SANS Institute and the National Institute of Standards and Technology under the US Department of Commerce (NIST).
The Secunia CSI 7.0 is the Total Package: Vulnerability Intelligence, Vulnerability Scanning with Patch Creation and Patch Deployment Integration.
Secunia CSI 7.0
To help IT teams counter the threat, vulnerability research company Secunia merges the in-house vulnerability expertise with a sophisticated patch management solution into the Secunia Corporate Software Inspector (CSI 7.0). The foundation of the Secunia CSI is a unique combination of vulnerability intelligence and vulnerability scanning, with patch creation and patch deployment integration.

Friday, 6 September 2013

Fake 'Grand Theft Auto V' Torrent Spreads Malware


Fake Grand Theft Auto V torrent spreading malware

Excitement continues .. Rockstar Games schedule the release of latest The Grand Theft Auto series, GTA 5 on September 17, but Cyber Criminals has already released a fake version of GTA 5 contains malware on torrent networks.
Romanian security firm BitDefender issued warning that GTA V hasn’t been leaked, and during installation you will be asked to complete a survey and send off a text message to gain the serial number. You will then be charged €1 per day on your phone bill and will be infected by a virus.
The PC version has yet to be announced, so trying to install it on your PC is a ridiculous idea; but that seems to be what a lot of people are doing.
"The survey opens in a web browser and, therefore, is able to perform a geographic redirect to the web page that corresponds to the area you are located in," said, Bitdefender Senior E-Threat Analyst Bogdan Botezatu.
This malware is a generic Trojan Trojan.GenericKDV.1134859, which can steal user information, tamper with system files or draft a computer into a botnet. This will result in you being charged for premium rate text messages sent by bogus firms.
The easiest way to avoid this malicious software is to not illegally download copies of GTA V, especially when the game isn't yet launched.

Code-sharing site GitHub now offers two-factor authentication to its users

Code repository GitHub offers two-factor authentication to beef up security around its users’ accounts. Github is a coding repository where developers used to build their projects projects that may turn out to be valued knowledgeable assets.
Two-Factor Authentication adds another layer of authentication to the login process, Now users have to enter their username and password, and a secret code in the second step, to complete the sign in. If a hacker manages to steal a user's credentials through phishing or trojans, cannot do anything, as they do need a second key to enter.
“We strongly urge you to turn on 2FA for the safety of your account, not only on GitHub, but on other websites that support it,” the company says. This two-factor authentication for Githu can be turned on in your account settings.
Code Repository %2527Github%2527 offers Two Factor Authentication
GitHub hit 3.5 million users’ landmark along with 6 million repositories deposited on its 5th anniversary in April. Two-factor authentication can protect you from phishing attacks, where hackers try to trick you into giving over your information.
For receiving the second authentication factor, users can either choose to receive it via a text message or can use dedicated authentication mobile app i.e. Google Authenticator for Android/iPhone/BlackBerry or Duo Mobile for Android/iPhone or Authenticator for Windows Phone 7.

Saturday, 31 August 2013

Fear of NSA PRISM : Indian Government may ban US email services for official communication

The Indian Government is planning to ban the use of US based email services like Gmail for official communications to increase the security of confidential government information.
The recent disconcerting reports that that India was being spied upon by American intelligence agencies has opened an all new chapter in the cyber security space. As leaked by former US National Security Agency contractor Edward Snowden, that NSA involved in widespread spying and surveillance activities across the globe.
The Government plans to send a formal notification to about 500,000 employees across the country, asking them to stick to the official email service provided by India's National Informatics Centre, Time of India Reported.
The fact that several government officers in top positions use their Gmail IDs for official communications i.e. Several senior government officials in India, including ministers of state for communications & IT Milind Deora and Kruparani Killi, have their Gmail IDs listed in government portals as their office email.
Last week, India's IT minister Kapil Sibal revealed that the new policy will enforce rules such as use of static IP addresses, virtual private networks and one-time passwords for accessing Indian government email services on all Indian officials who are stationed abroad.
“All Indian missions will use NIC servers which are directly linked to a server in India and that will keep government information safe.” Sibal said.

Thursday, 29 August 2013

FBI used Anonymous to attack foreign government systems, claims jailed hacker Hammond

Sentencing for former LulzSec leader Hector Xavier Monsegur, better known as "Sabu" , has again been delayed. Monsegur pleaded guilty to a dozen criminal counts two years prior and stands to face more a maximum sentence of more than 124 years.
Another Lulzsec Hacker Jeremy Hammond has claimed that the FBI used Sabu to coordinate attacks against foreign governments, by Anonymous hackers and Others.
The delays indicate that the FBI is not extracting information from Monsegur and this could mean that the hacker may be helping FBI with other covert operations as Jeremy Hammond claims.
Jeremy Hammond, released a statement on Thursday accusing the US government of asking Monsegur to encourage fellow hacktivists to infiltrate foreign government entities.
“What many do not know is that Sabu was also used by his handlers to facilitate the hacking of the targets of the government’s choosing including numerous websites belonging to foreign governments”, Hammond said.
“What the United States could not accomplish legally, it used Sabu, and by extension, me and my co-defendants, to accomplish illegally”, Hammond added.
"Why was the US using us to infiltrate the private networks of foreign governments? What are they doing with the information we stole? And will anyone in our government ever be held accountable for these crimes?"
Hammond pleaded guilty in May to hacking private intelligence firm Stratfor to expose millions of revelatory emails. The Illinois native faces up to 10 years in prison when he is sentenced, scheduled for 15th November.

Java 6 vulnerable to #0day exploit; added to Neutrino exploit kit

Hackers are using a new exploit for a bug in the out-of-date but popular Java 6 platform to attack victims, and has been added to a commercially available Neutrino exploit kit.
The use of Java 6 still is prevalent, opening up a significant number of users to the threat. F-secure analyst Timo Hirvonen warned about the exploit over Twitter, advising that he had found an exploit in the wild actively targeting an unpatched vulnerability in Java 6, named CVE-2013-2463.
The exploit's proof-of-concept was made public last week, prior to in-the-wild attacks surfacing on Monday. Oracle is aware of the hole but, since Java 6 is no longer supported, the company will not patch the issue.
The vulnerability lies in Java Runtime Environment's 2D sub-component, which is used to make two-dimensional graphics. Because no patch is available, the exploits provides cybercriminals and other attackers an effective vehicle to launch attacks targeting users and organizations using Java 6.
The Neutrino crimeware kit was first spotted in March 2013, when it was identified as the source of a series of attacks that were exploiting Java vulnerabilities to install ransomware on victims' PCs, freezing them until users paid a fine that was supposedly being levied by the FBI and other law enforcement agencies.
The impact of this threat may be less for usual Internet users than for organizations/entities, who may not be quick to migrate to the latest software version due to business and/or operational continuity issues. 
Users should update their Java installations to the latest revision of version 7, which does not suffer from the issue. Users who don’t need Java in their everyday tasks should uninstall the software altogether.

Monday, 26 August 2013

Pinterest Exploit exposes user information of 70 Million accounts

Critical Pinterest Exploit threatens the privacy of millions of users
Security researcher Dan Melamed has found a serious Pinterest Exploit that exposed user's information of over 70 Million accounts.
The security researcher Dan Melamed has found a Critical Pinterest Exploit that compromised the privacy of over 70 Million Users, the flaw allows hackers to view the email address of any user on Pinterest.
Pinterest is a very popular social media, over 70 million users including high profile figures and brands that ordinary use it, such a flaw could have a serious impact on their privacy. Dan has found the way to access to the information belonging to the owner of the Access token, as the researcher has shown it is possible to display them visiting the following URL.
https://api.pinterest.com/v3/users/me/?access_token=
MTQzMTYwMjozNTcxOTE5NTE2MDQyNjcxNzc6MnwxMzc3MDY4ODMyOjAtLTE2
ZWJjNDg4NzYxYTFmZWIwZmU0ODcxYzc3ZWUyN2E2YTdhOWNlN2I=
Substituting the "/me/" part of the link with the username of another Pinterest user it is possible to view its email address.
For example the following link shows the email address for user "pinterest" ... try your username , it works!
https://api.pinterest.com/v3/users/pinterest/?access_token=MTQzMTYwMjozNTcx
OTE5NTE2MDQyNjcxNzc6MnwxMzc3MDY4
ODMyOjAtLTE2ZWJjNDg4NzYxYTFmZWIwZmU0ODcxYzc3ZWUyN2E2YTdhOWNlN2I=
A black hat could use the Pinterest Exploit to retrieve all of the email addresses from a list of users for malicious purposes, lets' think for example to a spear phishing attack.
Dan also provided a simple solution to fix the Pinterest Exploit he has discovered, it is sufficient to to check the owner of the access token against the user whose information is being requested, in this way it is possible to prevent any abuse.
Dan Revealed that Pinterest Security Team is very efficient and careful with privacy issues, it has already confirmed that the Pinterest Exploit has been patched. Let's consider that the same Pinterest gave Dan permission to disclose the Pinterest Exploit differently from other company with similar security problems, they also included Dan's name in the Pinterest Heroes List.
Dan Melamed discovered the same type of security flaw in StumbleUpon, the researcher was able to view the full name, email address, age, gender, and location of its users, but the company never gave him permission to disclose the exploit, even after they patched it.
As highlighted by Dan flaws like Pinterest Exploit and StumbleUpon vulnerability would have allowed a hacker to collect over 100 million email addresses, security for social media is a serious issue.

Sunday, 25 August 2013

Hacker reported vulnerability in Kaspersky website, Demonstrated malware spreading technique


The cyber Security Analyst  'Ebrahim Hegazy' (@Zigoo0) Consultant at Q-CERT has found an "Unvalidated Redirection Vulnerability" in the website of the giant security solutions vendor "Kaspersky".
Ebrahim, who found a SQL Injection in "Avira" website last month, this time he found a Unvalidated Redirection Vulnerability that could be exploited for various purposes such as:
  • Cloned websites (Phishing pages)
  • It could also be used by Black Hats for Malware spreading
In the specific case what is very striking is that the link usable for the attacks is originated by a security firm like Kaspersky with serious consequences.

Would you trust a link from your security vendor? Absolutely Yes! But imagine your security vendor is asking you to download a malware!
To explain how dangerous the situation is when your security vendor is vulnerable, Ebrahim Hegazy sent me a video explaining the malware spreading scenario to simulate a Black Hat's exploiting Unvalidated Redirection Vulnerability in Kaspersky website to serve a malware.
"Since I'm working on Cyber security analysis, I've seen many methods of black-hats to spread links, maybe this link is for Exploit kits, Java Applet, flash exploits, or maybe a direct link to their EXE file. Let's take an example on the Facebook spreading techniques of the attackers, you may notice that "Mediafire" website was used lately in wide Malware spreading attack on Facebook.com,Which caused a wide infection, as the infected user will start to send links from Mediafire.com to his friends and since "Mediafire" is a trusted website/source for users so they simply click it and download the file!
But what if the links are coming from a very well known Security solutions vendor such as Kaspersky? For sure people will trust the links. So, through "Unvalidated Redirection Vulnerability" in Kaspersky, attackers will be able to spread a link coming from Kaspersky.com but when the user clicks on that link, he will get redirected to the attacker's website which would download at Malware on their machines or even download a "Rogue Antivirus" to steal financial information such as credit card information!" explained Ebrahim Hegazy.

After the researcher reported the vulnerability to Kaspersky team, it took about 2 months to fix the vulnerability, it is really a long time considering that if a hacker had found this flaw before Hagazy he could spread links using Kaspersky.com.
The consequences of unfixing of such vulnerability are critical
  • Wide infection - since the redirection is coming from a trusted source especially if the attacker registered a domain name similar to Kaspersky.com
  • Very bad reputation for Kaspersky company.
  • Your most trusted resource "Your Antivirus" will be your worst enemy! Would you trust anything else!

Monday, 20 May 2013

Indian Hackers are hacking into Pakistani computers

While the Syrian Electronic Army gets all the publicity and the US-China hacking campaigns are now well known, India and Pakistan quietly have their own thing going on. According to two anti-virus firms, ESET and Symantec, Pakistani government agencies have been targeted by spear-phishing attacks—fraudulent emails that trick people into giving up sensitive information—from India for at least two and as long as four years.
Targets receive an email with attached Microsoft Word or pdf documents, with names like pakistandefencetoindiantopmiltrysecreat.pdf (Pakistan defense to Indian top military secret) and pakterrisiomforindian.pdf (Pak terrorism for Indian). The contents of the documents supposedly outline  ”India’s ambitious defense policy” and its plans to “fight China and Pakistan at the same time.” Despite the far-fetched nature of the latter scenario, enough people opened the files, which contained malicious code that installed itself on their machines. More baffling yet, they were impressed enough to forward the files on to other hapless victims.
Once installed, the malware can, among other things, log the user’s keystrokes (and thus record messages or passwords), take screenshots of the infected computer’s screen, copy itself to memory sticks, and connect to a remote server from which the computer can be controlled or have more information sucked out of it. But it isn’t a particularly sophisticated attack. According to ESET, the attackers used publicly available tools, allowed the code to add an item to the computer’s system menu (meaning that an alert user would notice something suspicious) and didn’t bother encrypting communications to their server. ESET speculates that the reason for the clumsy approach may be that nothing fancier was needed.
Pakistan is not the only country attacked, though it is host to 80% of ESET’s detections. Among others countries affected are the US, Brazil, Russia and India itself. Although it is hard to prove the attacks originated in India, ESET pointed to timestamps found by its researchers that matched Indian working hours. More incriminatingly, some of the variables within the code were named after Indianisms. One was called “ramukaka”—Ramu is a nickname and kaka means uncle. Another was “malibaba”: Mali is a surname and also a common noun for gardener, while baba is a suffix generally used  to address baby boys.