Showing posts with label exploit. Show all posts

Monday, 13 January 2014

How to hack a Wireless DSL Router, Exploit posted online


Hack Wireless DSL Router

A hacker from France named “Eloi Vanderbeken”found a way to hack NetGear and Linksys wireless routers on Christmas, and as well as, he distributed that secret exploit in public also.
The secret exploit allows an attacker to change the admin panel password to default without any admin authentication.

Eloi forgot his Linksys WAG200G router’s password and was trying to crack that , he scanned that and found a suspicious open TCP port. He researched on the part deeply and downloaded the copy Linksys firmware and then reverse-engineered that.

After a research 0n that port, he found that was a secret backdoor that allows anyone to send commands on admin basis without admin authentication. Well, it’s a cool exploit for- who really forgot the password, but may be dangerous for them where- Near-by “Hackers situated.”

 Eloi tried to describe you what and how he found the secret exploit, below are the routers which are affected by the Exploit:
  • Cisco RVS4000 fwv 2.0.3.2
  • Cisco WAP4410N
  • Cisco WRVS4400N
  • Cisco WRVS4400N
  • Diamond DSL642WLG / SerComm IP806Gx v2 TI
  • LevelOne WBR3460B
  • Linksys RVS4000 Firmware V1.3.3.5
  • Linksys WAG120N
  • Linksys WAG160n v1 and v2
  • Linksys WAG200G
  • Linksys WAG320N
  • Linksys WAG54G2
  • Linksys WAG54GS
  • Linksys WRT350N v2 fw 2.00.19
  • Linksys WRT300N fw 2.00.17
  • Netgear DG834[, GB, N, PN, GT] version < 5
  • Netgear DGN1000
  • Netgear DGN1000[B] N150
  • Netgear DGN2000B
  • Netgear DGN3500
  • Netgear DGND3300
  • Netgear DGND3300Bv2 fwv 2.1.00.53_1.00.53GR
  • Netgear DM111Pv2
  • Netgear JNR3210
May be affected:
  • all SerComm manufactured devices
  • Linksys WAG160N
  • Netgear DG934 probability: probability: 99.99%
  • Netgear WG602, WGR614 (v3 doesn’t work, maybe others…)
  • Netgear WPNT834
Here is the Exploit code, if you are looking for, and you can find a detailed list of routers which are affected or not HERE.

Friday, 8 November 2013

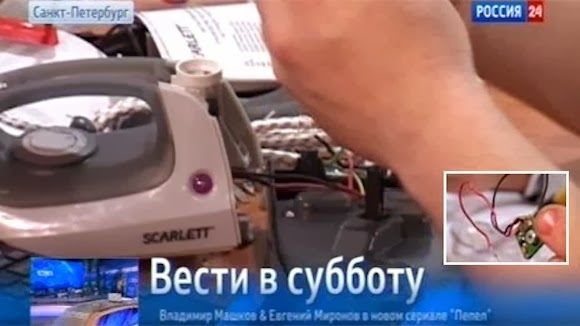
Russia: Chinese planting hidden chips in Irons & electric kettles which serve malware in systems

Chinese hidden chip in iron


How will you react when you will came to know—your Chinese Iron has inbuilt chip which is being used to server malware on to your systems, well if you talk mine then i will throw that outside and will call that “The NSA Aunty.”

A Russian TV Rossiya 24 reported about this Malware machine even they showed footage of technician while opening the Iron included in a batch of Chinese imports to find a “spy chip” with what he called “a little microphone”.

These types of hidden chips are being used to spread viruses through connecting to any computer with in a 200m (656ft) radius which were using unprotected Wi-Fi networks. Other components like mobile phones and car dashboard cameras are also affected with this hidden chip, the Russian TV reported.

One thing also reported by the channel that these hidden chips look small, but had been attacked company networks, sending out spam without administrators’ knowledge.

According to a news agency the latest order of these irons have been cancelled but more than 30 devices had already been sent to retailers in St. Petersburg.

From now, would you like to bring that NSA aunty to your home, tell us in comments, we like to hear from you.

Tuesday, 15 October 2013

Vulnerability in WhatsApp allows decrypting user messages

WhatsApp
A serious vulnerability in WhatsApp allows anyone who is able to eavesdrop on WhatsApp connection to decrypt users' messages.
Whatsapp, the mobile application for instant messaging platform has become one of the main communication tools of the present day and its popularity makes it attractive for security researchers and hackers.
This time it is debated in the protection of the messages exchanged through the application, thanks to a vulnerability in the crypto implementation they can be intercepted by an attacker.
Thijs Alkemade is a computer science student at Utrecht University in The Netherlands who works on the open source Adium instant messaging project, during its research activity he disclosed a serious issue in the encryption used to secure WhatsApp messages.
In the post titled "Piercing Through WhatsApp’s Encryption" Alkemade remarked that Whatsapp has been plagued by numerous security issues recently, easily stolen passwords, unencrypted messages and even a website that can change anyone’s status.
"You should assume that anyone who is able to eavesdrop on your WhatsApp connection is capable of decrypting your messages, given enough effort. You should consider all your previous WhatsApp conversations compromised. There is nothing a WhatsApp user can do about this but expect to stop using it until the developers can update it." states the researcher.
An attacker sniffing a WhatsApp conversation is able to recover most of the plaintext bytes sent, WhatsApp uses RC4 software stream cipher to generate a stream of bytes that are encrypted with the XOR additive cipher.
Vulnerability in WhatsApp allows decrypting user messages

The mistakes are:
  • The same encryption key in both directions
  • The same HMAC key in both directions
Below the trick used by the researcher to reveal the messages sent with WhatsApp exploiting first issue:
WhatsApp adopts the same key for the incoming and the outgoing RC4 stream, "we know that ciphertext byte i on the incoming stream xored with ciphertext byte i on the outgoing stream will be equal to xoring plaintext byte i on the incoming stream with plaintext byte i of the outgoing stream. By xoring this with either of the plaintext bytes, we can uncover the other byte."
The technique doesn't directly reveal all bytes but works in many cases, another element that advantage the attacker is that messages follow the same structure and are easy to predict starting from the portion of plaintext that is disclosed.
The second issue related to the HMAC id more difficult to exploit, Alkemade said WhatsApp also uses the same HMAC key in both directions, another implementation error that puts messages at risk, but is more difficult to exploit.
The MAC is used to detect data alteration but it is not enough to detect all forms of tampering, the attacker potentially could manipulate any message.
"TLS counters this by including a sequence number in the plaintext of every message and by using a different key for the HMAC for messages from the server to the client and for messages from the client to the server. WhatsApp does not use such a sequence counter and it reuses the key used for RC4 for the HMAC."
Alkemade is very critical to the development team of the popular platform:
There are many pitfalls when developing a streaming encryption protocol. Considering they don’t know how to use a xor correctly, maybe the WhatsApp developers should stop trying to do this themselves and accept the solution that has been reviewed, updated and fixed for more than 15 years, like TLS,” he said.
I agree with the thinking of the researcher, security for applications such as WhatsApp is crucial given its level of penetration, it is true that the interest of the scientific community and cybercrime will surely lead them to discover new vulnerabilities to which WhatsApp have to provide a quick solution.
Alkemade confirmed that there is no remediation for the flaw in this moment, that's why he suggest to stop using WhatsApp until developers produce a patch.

Monday, 26 August 2013

Pinterest Exploit exposes user information of 70 Million accounts

Critical Pinterest Exploit threatens the privacy of millions of users
Security researcher Dan Melamed has found a serious Pinterest Exploit that exposed user's information of over 70 Million accounts.
The security researcher Dan Melamed has found a Critical Pinterest Exploit that compromised the privacy of over 70 Million Users, the flaw allows hackers to view the email address of any user on Pinterest.
Pinterest is a very popular social media, over 70 million users including high profile figures and brands that ordinary use it, such a flaw could have a serious impact on their privacy. Dan has found the way to access to the information belonging to the owner of the Access token, as the researcher has shown it is possible to display them visiting the following URL.
https://api.pinterest.com/v3/users/me/?access_token=
MTQzMTYwMjozNTcxOTE5NTE2MDQyNjcxNzc6MnwxMzc3MDY4ODMyOjAtLTE2
ZWJjNDg4NzYxYTFmZWIwZmU0ODcxYzc3ZWUyN2E2YTdhOWNlN2I=
Substituting the "/me/" part of the link with the username of another Pinterest user it is possible to view its email address.
For example the following link shows the email address for user "pinterest" ... try your username , it works!
https://api.pinterest.com/v3/users/pinterest/?access_token=MTQzMTYwMjozNTcx
OTE5NTE2MDQyNjcxNzc6MnwxMzc3MDY4
ODMyOjAtLTE2ZWJjNDg4NzYxYTFmZWIwZmU0ODcxYzc3ZWUyN2E2YTdhOWNlN2I=
A black hat could use the Pinterest Exploit to retrieve all of the email addresses from a list of users for malicious purposes, lets' think for example to a spear phishing attack.
Dan also provided a simple solution to fix the Pinterest Exploit he has discovered, it is sufficient to to check the owner of the access token against the user whose information is being requested, in this way it is possible to prevent any abuse.
Dan Revealed that Pinterest Security Team is very efficient and careful with privacy issues, it has already confirmed that the Pinterest Exploit has been patched. Let's consider that the same Pinterest gave Dan permission to disclose the Pinterest Exploit differently from other company with similar security problems, they also included Dan's name in the Pinterest Heroes List.
Dan Melamed discovered the same type of security flaw in StumbleUpon, the researcher was able to view the full name, email address, age, gender, and location of its users, but the company never gave him permission to disclose the exploit, even after they patched it.
As highlighted by Dan flaws like Pinterest Exploit and StumbleUpon vulnerability would have allowed a hacker to collect over 100 million email addresses, security for social media is a serious issue.